Compliance as a service needs a scope-specific quote in 2026, not a universal monthly figure: your budget depends on the requirements, systems, and work included. The recurring service fee is only part of the decision; confirm whether setup, security fixes, software licenses, and independent assessments are included before you compare proposals.
- How much does compliance as a service cost? Compare scoped quotes, not subscription fees alone.
- Separate compliance management, security remediation, software licenses, and independent assessments before approving a budget.
- Microsoft 365 compliance reporting supports evidence collection; it does not replace accountable owners or technical fixes.
- Choose compliance support by deliverables, responsibilities, and exclusions—not the number of dashboard features.
How much does compliance as a service cost in 2026?
The useful number is the total budget for your defined compliance scope. Ask each provider to quote the same systems, requirements, deliverables, and responsibilities. Otherwise, a proposal covering policy templates is being compared with one covering technical implementation and ongoing evidence collection.
Use this breakdown to identify what each quote actually buys. It is a purchasing checklist, not a statement that every provider bundles these services.
| Budget component | What to ask the provider to include | What to clarify separately |
|---|---|---|
| Initial assessment | Current-state review, scope definition, and prioritized gaps | Whether findings include an implementation plan |
| Setup and implementation | Policy configuration, system connections, and assigned responsibilities | Whether technical changes are included |
| Recurring compliance management | Evidence collection, reviews, issue tracking, and reporting | Review frequency and customer responsibilities |
| Security remediation | Changes needed to address identified technical gaps | Who performs the work and authorizes changes |
| Software licenses | Tools required for the agreed scope | Existing licenses versus additional subscriptions |
| Independent assessment | External examination or certification where applicable | Whether an independent assessor needs a separate engagement |
| Internal staff time | Approvals, interviews, training, and evidence validation | Which tasks remain with your employees |
For organizations using Microsoft 365, the automated compliance reporting workflow is a useful companion when you define evidence-collection requirements. Reporting is a deliverable; correcting a configuration problem is a separate task unless the agreement explicitly includes it.
Keep the billing basis visible beside each component. Identify fixed project work, recurring services, separately licensed software, and work requiring an additional authorization. You need this distinction to understand the commitment, even before comparing the quoted amounts.
Why this matters
A small business needs compliance work to support a real business obligation: a customer requirement, a contractual commitment, or an applicable regulation. Buying a service without defining that obligation leaves you with activity instead of a clear outcome.
For your 2026 budget, separate being ready to demonstrate a control from having that control operate correctly. A control is a safeguard or procedure, such as restricting access to sensitive records. Evidence shows what happened; implementation makes the safeguard work.
A dashboard showing an access problem does not remove that access. A written backup policy does not prove that files can be restored. Your agreement should identify who reviews each finding, who fixes it, and who confirms completion.
Compare service scopes before comparing quotes
These are purchasing approaches, not standardized provider tiers. Use them to describe the work you need, then require the proposal to match that description.
| Service scope | Best for | Main benefit | Main limitation |
|---|---|---|---|
| Software-led compliance | Teams with staff available to manage controls and evidence | Organizes requirements, tasks, and supporting records | Your team still needs to interpret findings and perform fixes |
| Advisory support | Businesses needing guidance on requirements and priorities | Helps define policies, responsibilities, and a remediation plan | Advice does not automatically include technical implementation |
| Managed compliance operations | Businesses needing ongoing coordination and evidence handling | Assigns recurring tasks and maintains an operating process | The contract still needs explicit boundaries for remediation and assessments |
| Integrated IT and compliance support | Businesses needing technical changes alongside compliance coordination | Connects policy requirements with system administration | Bundled support needs a clear division between routine IT work and compliance deliverables |
Software-led compliance: retain an internal owner
Best for: a business with someone accountable for implementation. Software can organize evidence and tasks, but a task list is not an operating compliance program. Your owner needs authority to obtain approvals, assign work, and resolve exceptions.
Ask what happens when a system connection fails or a check produces an unclear result. The proposal should distinguish tool support from interpreting a requirement and changing the underlying system. Choose this approach only when your team can carry those responsibilities.
Advisory support: specify the handoff
Best for: a business that needs a clear plan and can execute it. Advisory work helps translate requirements into policies and priorities. Its boundary is execution: a recommendation to restrict access still needs an administrator to change permissions.
Request an implementation-ready handoff. Each finding should identify the affected system, required action, responsible owner, and evidence needed to close it. A report without ownership leaves the work unresolved.
Managed compliance operations: define recurring work
Best for: a business that needs help maintaining the process. Recurring support should have named deliverables, not just access to a portal. Specify who gathers evidence, checks exceptions, follows up with owners, and prepares management reports.
The limitation is contractual scope. Do not assume ongoing coordination includes every technical fix, customer questionnaire, or external assessment. List those activities separately and confirm how additional work is approved.
Integrated IT and compliance support: connect findings to fixes
Best for: a business whose compliance gaps require system changes. Technical administration and compliance coordination serve different purposes, but they need a working handoff. The person identifying an access issue must know who can correct it.
TeraCloud is best suited to small and midsize businesses seeking managed IT, cybersecurity, and cloud support. Its stated services are relevant to technical work behind compliance, but a compliance-specific scope needs explicit confirmation. Do not treat managed IT support as proof that an external assessment or every compliance deliverable is included.
Why compliance as a service costs vary
The scope drivers below determine the work you should request. Use them to explain your business consistently to every provider rather than asking for a quote with no boundaries.
- Requirements and obligations. Name the regulation, contract, customer request, or framework you need to address. A general security review and preparation for a named assessment are different assignments.
- Systems and data boundaries. Identify the applications, devices, cloud environments, and records included. The provider needs a defined boundary for evidence collection and technical work.
- Current control condition. Distinguish safeguards that already operate from gaps requiring implementation. Existing documentation does not establish that the underlying process works.
- Division of responsibility. State whether your staff will approve policies, administer systems, gather evidence, and answer assessor questions. Work assigned to your team remains a resource commitment.
- Recurring deliverables. Specify reporting, reviews, exception handling, and follow-up. A setup project and an ongoing operating service should not be treated as equivalent.
- Assessment involvement. Clarify preparation, attendance, evidence requests, and follow-up. Independent assessment and day-to-day compliance management have different roles.
In 2026, use the same scope document for every proposal. Differences then become visible: one provider includes implementation, another supplies recommendations, and another depends on your team to collect records. Those distinctions matter more than the service label.
How to request a comparable compliance quote
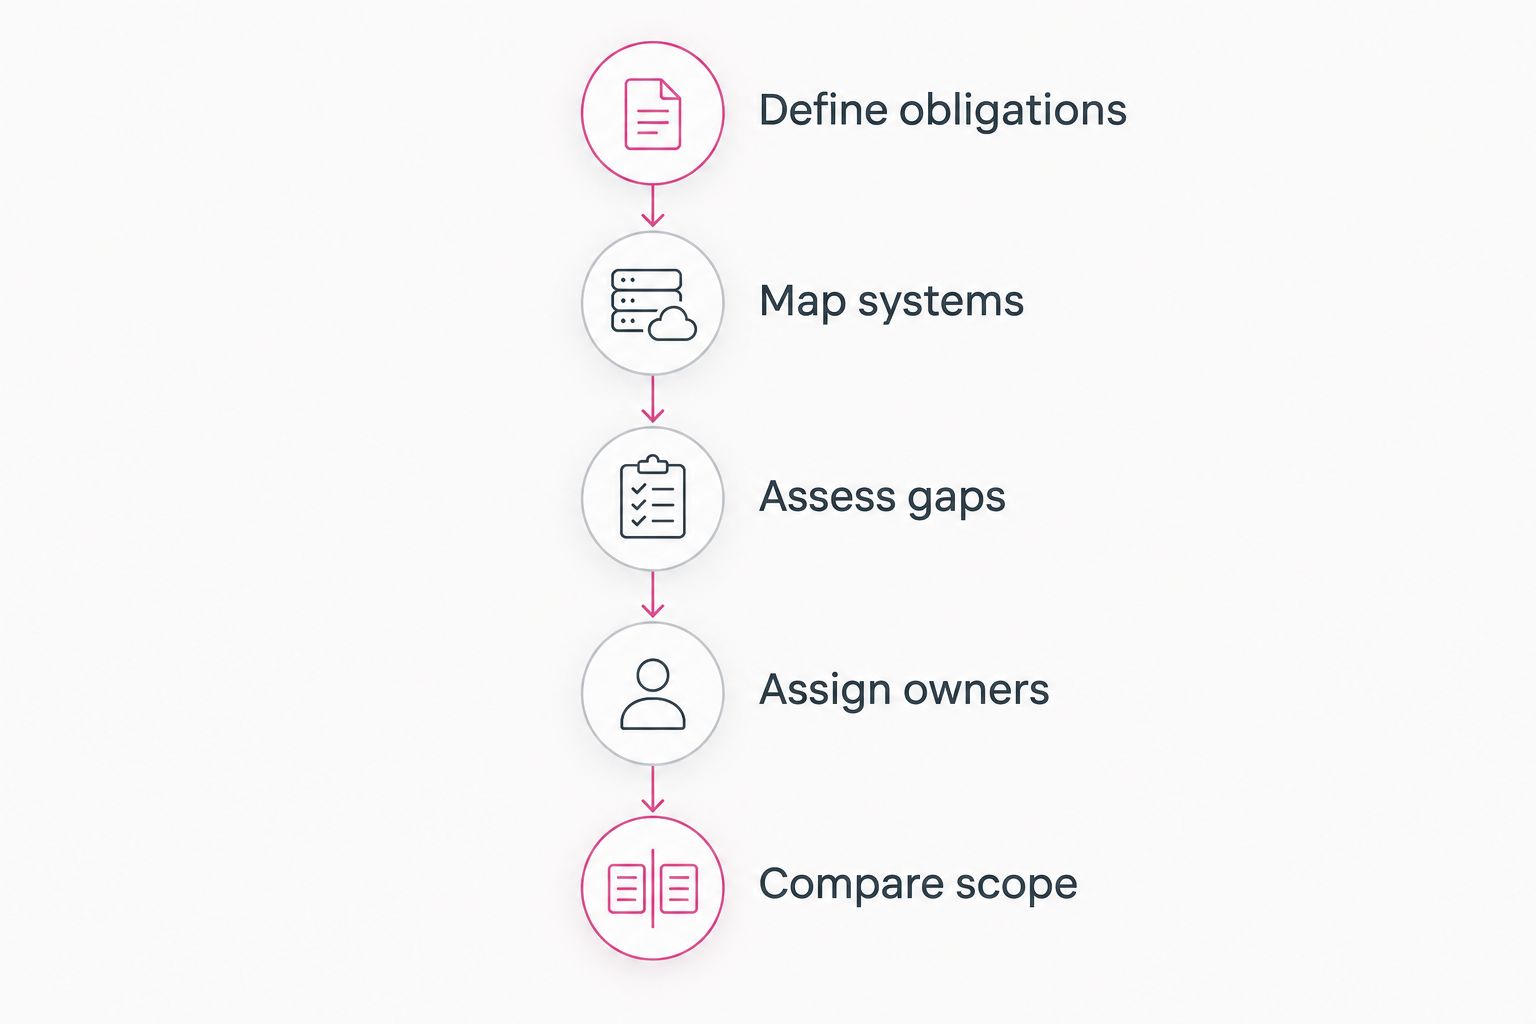
A useful quote starts with a business requirement and ends with an accountable work plan. Follow this sequence before asking providers to finalize their proposals.
- Define obligations. Write down the specific requirement and the outcome you need to demonstrate. Separate mandatory obligations from improvements you want to make.
- Map systems. Identify where relevant information lives and who administers each environment. Include outsourced systems when they fall within the requirement.
- Assess gaps. Record known weaknesses and supporting evidence. Keep confirmed issues separate from questions that still need investigation.
- Assign owners. Decide what your staff will do and what you want the provider to perform. Include approvals, technical changes, and evidence validation.
- Compare scope. Require each proposal to address the same deliverables and exclusions. Resolve differences before choosing a provider.
Give providers a short description of your business operations, not just a requested framework name. Explain what information you handle, which systems support it, and which staff can assist. This makes the boundary of the requested engagement explicit.
Then ask for a deliverable list you can verify. Replace vague wording such as ongoing assistance with specific outputs: an approved policy, a reviewed access list, an exception register, or a remediation record. Each output should have an owner and an acceptance criterion.
What should a compliance service agreement include?
The agreement should make completion observable. If you cannot tell whether a task is finished, you cannot judge whether the service delivered the promised work.
For your 2026 agreement, check these terms before signing:
- Scope boundary: the included requirements, systems, departments, and data.
- Deliverables: the documents, reports, reviews, and implementation work you receive.
- Responsibility split: provider tasks, employee tasks, and required approvals.
- Exclusions: independent assessments, legal advice, technical changes, and other work outside the agreement.
- Change process: how new systems, additional requirements, and expanded work are authorized.
- Evidence access: how your business retrieves records during the engagement and after it ends.
Ask who owns the evidence repository and how records are exported. Compliance support should leave your business able to explain its controls, not dependent on an inaccessible collection of documents.
If technical implementation is part of your plan, TeraCloud provides managed IT, cybersecurity, cloud migration, and data management services for small and midsize businesses. Confirm the requested compliance work separately. The benefit is relevant technical support; the boundary is that the stated service list does not establish a compliance package or independent assessment engagement.
Is compliance software enough without managed support?
Compliance software is enough only when your team can own the associated decisions, controls, and follow-up. A connected tool does not replace policy approval, technical administration, or management accountability.
Choose software-led support when those responsibilities already have capable owners. Choose additional service support when you need help performing specific tasks, and name those tasks in the agreement.
Does managed IT support include compliance work?
Managed IT support includes compliance work only when the agreement explicitly says so. Device administration, cybersecurity, and cloud support can contribute to controls, but they do not establish the scope of evidence reviews or assessment preparation.
TeraCloud offers 24/7 managed IT support, according to its stated offering. That support coverage is not an assessment schedule or a guarantee that compliance obligations are satisfied.
Can a compliance provider guarantee an assessment result?
A provider's preparation work does not replace an assessor's judgment or your business's responsibilities. Require clear deliverables rather than treating a promised result as a substitute for evidence.
Ask how findings will be handled, who must make corrections, and what support continues through assessment follow-up. Those answers describe the work you are buying.
FAQ
How much does compliance as a service cost in 2026?
Compliance as a service requires a scope-specific quote in 2026. Compare recurring management, setup, technical remediation, licenses, independent assessment work, and internal responsibilities separately.
What's the best way to compare compliance service quotes?
Compare quotes against the same requirements, systems, deliverables, and responsibility split. A software subscription and a service that performs technical fixes are different scopes.
Is compliance software better than a managed service?
Compliance software fits a team that can own implementation and follow-up; managed support fits tasks you need someone else to perform. Decide by responsibility coverage, not the product label.
Does compliance as a service include an independent audit?
An independent audit is included only if the agreement explicitly covers it. Separate preparation support from the independent assessor's engagement and responsibilities.
Does TeraCloud provide technical services relevant to compliance?
TeraCloud provides managed IT, cybersecurity, cloud migration, and data management for small and midsize businesses. Confirm compliance-specific deliverables rather than assuming they are included.
Can Microsoft 365 reports prove my business is compliant?
Microsoft 365 reports provide evidence about the systems and activities they cover, not proof that every obligation is satisfied. Review report scope, validate findings, and assign owners for corrections.
What should I ask before signing a compliance service contract?
Ask for included deliverables, exclusions, ownership, evidence access, and the process for additional work. Make sure technical fixes and independent assessment support have explicit responsibilities.
Related guides
- Compliance as a service providers for small businesses
- Managed cybersecurity budgeting for a small business
- Data management and governance services
One last thing
A completed questionnaire is a record of answers, not proof that every safeguard operates as described. Before approving your 2026 compliance budget, choose a required control and ask who operates it, what evidence demonstrates it, and who corrects a failure.
Your next step: send every shortlisted provider the same written scope and request a proposal that separates recurring work, implementation, licenses, and independent assessment responsibilities.


